Hollys Coffee data breach: 2.76 million customer records stolen in cyberattack
Synopsis
South Korean coffee chain Hollys has confirmed hackers stole 2.76 million pieces of customer data over a five-week window — the latest hit in a cascade of cyberattacks that has already swept through 16 of the country's financial institutions, exposing around 100,000 records. South Korea is confronting a systemic data-security crisis across both retail and banking sectors.
Key Takeaways
Hollys Coffee confirmed a breach of 2.76 million customer records, including dates of birth, phone numbers, addresses, and emails.
The hack occurred between September 3 and October 7, 2026 , when unauthorised access was detected.
The company said the stolen data came from temporary files from a past membership overhaul, not the live customer database.
Hollys operates approximately 530 outlets across South Korea and is owned by conglomerate KG Group .
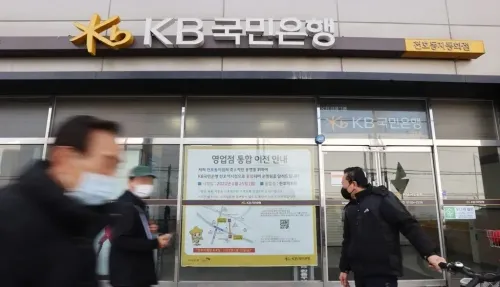
The breach follows attacks on 16 South Korean financial institutions , with around 100,000 cases of leaked personal data reported, including at KB Kookmin Bank and Shinhan Bank .
The Financial Services Commission (FSC) confirmed that bank account and credit card numbers were not among the leaked financial sector data.
South Korean coffee chain Hollys has confirmed that 2.76 million pieces of customer personal information were stolen by hackers, making it the latest victim in a growing wave of cyberattacks targeting local companies in South Korea. The franchise disclosed the breach on Monday, 19 October, through a notice posted on its official website.
What Was Stolen and When
According to the company's disclosure, hackers accessed its membership programme systems over a period spanning September 3 to October 7, when Hollys detected the unauthorised intrusion. The stolen data reportedly includes customers' dates of birth, phone numbers, addresses, and email addresses.
Hollys clarified that the compromised data was not drawn from its live customer database. 'We understand that the leaked data consists of temporary data files provided for a past membership service overhaul, not the data from the currently active customer database,' the company said in its notice, adding that the full scope of the incident is still under investigation.
Company Apology and Response
'We sincerely apologize for causing customer concern from this incident. We will make our utmost efforts to protect customer data and minimize damage from the breach,' the company stated. Hollys said it is continuing to investigate and has not yet issued a timeline for completing its assessment.
Hollys currently operates around 530 outlets across South Korea and is owned by KG Group, a domestic conglomerate with business interests spanning steelmaking, car manufacturing, and logistics services.
Part of a Broader Wave of Attacks on South Korean Firms
The Hollys breach follows a series of recent cyberattacks on South Korean financial institutions. Around 100,000 cases of leaked personal information — including names, email addresses, and phone numbers — are presumed to have occurred across 16 financial institutions in a string of hacking incidents, according to financial regulators as of last Friday.
Among the affected institutions are major lenders KB Kookmin Bank and Shinhan Bank, which reported back-to-back data leaks earlier this month. The Financial Services Commission (FSC) confirmed that those affected institutions are conducting reviews to determine whether additional breaches have occurred. Notably, the FSC stated that bank account numbers, credit card numbers, and other sensitive financial data were not compromised in the financial sector attacks.
What This Signals for Corporate Cybersecurity in South Korea
The cluster of breaches — spanning retail food chains and major banks — points to a systemic vulnerability in how South Korean companies handle membership and customer data systems, particularly legacy or transitional databases. Regulators and analysts are likely to scrutinise data retention practices in the wake of these incidents. With investigations still ongoing at both Hollys and the affected financial firms, the final tally of exposed records could rise further in the coming weeks.
Point of View
The kind of data that companies often deprioritise after a platform migration. Regulators globally have pushed for mandatory deletion of stale data, yet companies routinely retain it in limbo. South Korea's FSC has moved quickly to audit financial institutions, but consumer-facing retail chains operate under lighter oversight — a gap that this incident exposes sharply. With 16 financial firms already compromised and now a major coffee chain, the pattern suggests coordinated or opportunistic actors probing multiple sectors simultaneously, which warrants a national-level response beyond institution-by-institution audits.
NationPress
19 Oct 2026
Frequently Asked Questions
What happened in the Hollys Coffee data breach?
Hackers accessed Hollys Coffee's membership programme systems between September 3 and October 7, 2026, stealing 2.76 million pieces of customer personal information, including dates of birth, phone numbers, addresses, and email addresses. The company disclosed the breach on 19 October 2026 via a notice on its website.
Was the live Hollys customer database compromised?
According to Hollys, the stolen data came from temporary files associated with a past membership service overhaul, not from the currently active customer database. The company said it is still investigating the full scope of the incident.
How does the Hollys breach relate to recent South Korean financial sector attacks?
The Hollys breach follows a series of cyberattacks on 16 South Korean financial institutions, including KB Kookmin Bank and Shinhan Bank, in which around 100,000 cases of personal data leaks are presumed to have occurred. Together, the incidents suggest a broader pattern of coordinated hacking activity targeting South Korean companies across sectors.
Were bank account or credit card numbers leaked in the financial sector attacks?
No. The Financial Services Commission (FSC) confirmed that bank account numbers, credit card numbers, and other sensitive financial data were not among the information leaked in the attacks on South Korean financial institutions. Affected banks are still reviewing whether additional breaches occurred.
Who owns Hollys Coffee and how large is the chain?
Hollys is owned by KG Group, a South Korean conglomerate with operations spanning steelmaking, car manufacturing, and logistics. The chain currently operates around 530 outlets across South Korea.