South Korea banks to raise cybersecurity spend after AI-assisted hacking hits Shinhan, Hana, KB
Synopsis
South Korea's three biggest banks — Shinhan, Hana, and KB Kookmin — were hit by AI-powered hackers in October 2026, leaking data of at least 25,000 customers. Now the president is demanding answers, police have expanded their probe to cover 12 countries' IP addresses, and the banks are racing to spend their way to safety — with KB alone planning to cross ₩100 billion in cybersecurity outlay by 2027.
Key Takeaways
Shinhan Bank disclosed on 1 October 2026 that data of approximately 25,000 customers — names, phone numbers, and annual incomes — was leaked using AI-assisted hacking tools .
Hana Bank and KB Kookmin Bank also reported similar data exposure incidents this month.
KB Kookmin Bank plans to raise its cybersecurity budget to over 100 billion won (US$74 million) in 2027 , up from 86.07 billion won in 2026.
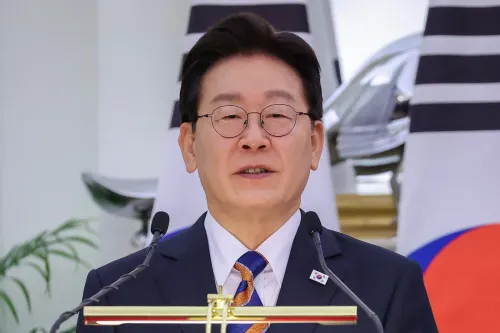
President Lee Jae Myung called for a thorough investigation; the Financial Supervisory Service (FSS) identified suspect IP addresses in 12 countries .
The National Office of Investigation added 15 personnel to its existing 28-member cyber probe team.
South Korean banks are moving to significantly increase cybersecurity budgets and headcount after a wave of AI-assisted hacking attacks struck major lenders this month, exposing customer data and prompting a government-level response. The incidents at Shinhan Bank, Hana Bank, and KB Kookmin Bank have raised serious concerns about the scale and sophistication of the breaches, according to industry sources.
What the Breaches Revealed
On 1 October 2026, Shinhan Bank disclosed that personal information belonging to approximately 25,000 customers — including names, phone numbers, and annual incomes — had been leaked. The hackers reportedly deployed advanced artificial intelligence (AI) tools to carry out the attack, marking a notable escalation in the methods used against financial institutions. Similar data leaks or customer information exposures were also reported at other banks, though the full scale of those incidents remains under assessment.
How Banks Plan to Respond
KB Kookmin Bank plans to raise its cybersecurity budget to more than 100 billion won (approximately US$74 million) in 2027, up from 86.07 billion won this year, according to industry sources. Shinhan Bank is reportedly set to allocate a record cybersecurity budget, while Hana Bank plans to invest tens of billions of won in bolstering its security infrastructure next year. All three lenders also intend to expand their cybersecurity personnel in 2026–27.
Government Steps In
South Korean President Lee Jae Myung called over the weekend for a thorough investigation into the attacks. The Financial Supervisory Service (FSS) subsequently identified Internet Protocol (IP) addresses across 12 countries that are suspected of being linked to the AI-assisted hacking campaign, though investigators were reportedly unable to determine physical locations tied to some of those addresses. South Korean police confirmed on Friday that they have assigned additional personnel to the probe, with the National Office of Investigation adding 15 more investigators to an existing 28-member team looking into the attacks against multiple financial companies.
Wider Implications for Financial Security
This comes amid a globally documented rise in AI-enhanced cyberattacks targeting financial institutions, where machine learning tools are increasingly used to automate phishing, bypass authentication, and accelerate data exfiltration. Notably, the simultaneous breach of three major South Korean lenders within a single month signals a coordinated campaign rather than isolated incidents. The cross-border nature of the IP trail — spanning 12 countries — complicates attribution and underscores the limits of domestic law enforcement in countering internationally orchestrated cyber threats. Investigators have not yet publicly attributed the attacks to any specific actor or nation-state.
What Comes Next
With the expanded investigation team now in place and bank budgets set to rise sharply, the key question is whether reactive spending can keep pace with attackers who are already leveraging next-generation tools. Cybersecurity experts have long argued that financial institutions need continuous red-team exercises and AI-native defence systems — not just periodic budget increases — to meaningfully reduce breach risk. South Korea's financial regulators and law enforcement are expected to provide further updates as the cross-border IP investigation progresses.
Point of View
But attribution in AI-enabled attacks is notoriously difficult and the trail frequently ends in dead ends. More critically, the banks' response — bigger budgets — is the traditional playbook, and it has a mixed track record. The real gap is not spend, but adaptive defence architecture; no budget figure fixes that without a parallel overhaul of detection and response protocols.
NationPress
11 Oct 2026
Frequently Asked Questions
Which South Korean banks were affected by the AI-assisted hacking attacks?
Shinhan Bank , Hana Bank , and KB Kookmin Bank all reported data leaks or customer information exposure in October 2026. Shinhan Bank confirmed the leak of personal data belonging to approximately 25,000 customers, with hackers reportedly using advanced AI tools in the attack.
What data was stolen in the Shinhan Bank hack?
Shinhan Bank disclosed on 1 October 2026 that approximately 25,000 customers' names, phone numbers, and annual incomes were leaked. The bank attributed the breach to hackers using advanced artificial intelligence tools.
How much are South Korean banks increasing their cybersecurity budgets?
KB Kookmin Bank plans to increase its cybersecurity budget to more than 100 billion won (US$74 million) in 2027, up from 86.07 billion won in 2026. Shinhan Bank plans a record cybersecurity allocation, and Hana Bank plans to invest tens of billions of won in security upgrades next year.
What is the South Korean government doing in response to these hacking incidents?
President Lee Jae Myung called for a thorough investigation over the weekend. The Financial Supervisory Service (FSS) identified suspect IP addresses in 12 countries , and the National Office of Investigation expanded its probe team by adding 15 investigators to the existing 28-member unit.
Why are AI-assisted cyberattacks on banks particularly dangerous?
AI tools allow attackers to automate data exfiltration, bypass standard authentication systems, and scale attacks faster than conventional defences can respond. The coordinated breaches of multiple major South Korean lenders within a single month suggest a sophisticated, possibly state-linked campaign — though no attribution has been confirmed by investigators.