South Korea cyber breaches hit banks, govt agencies, 100,000 records exposed
Synopsis
South Korea's digital economy is under siege — 16 financial firms breached, 100,000 customer records compromised, and the personal data of President Lee Jae Myung and Cabinet ministers leaked from a presidential aircraft manifest. With AI-powered hackers accelerating attacks faster than organisations can respond, the NIS has ordered emergency checks at 2,100 agencies. The question now is whether the country's crisis response can outrun the threat.
Key Takeaways
Cyberattacks have been confirmed at 16 financial firms in South Korea , compromising approximately 100,000 customer records as of 14 October .
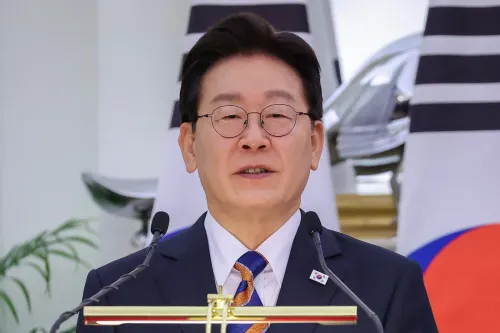
Personal data of 168 individuals — including President Lee Jae Myung and Cabinet ministers — was leaked from the presidential aircraft manifest; police have launched an investigation.
The National Intelligence Service (NIS) has ordered emergency security inspections at 2,100 government agencies , to be completed by mid-November .
Daishin Securities , Mirae Asset Global Investments and Bithumb each reported separate breaches on 28 October .
The Ministry of Science and ICT raised the cyber crisis warning level to 'caution' and plans to inspect 170 private-sector IT infrastructure facilities .
Experts warn AI-powered attacks are escalating faster than organisations can patch vulnerabilities, raising systemic risk across manufacturing, finance and telecoms.
South Korea is grappling with a sustained wave of cyberattacks targeting banks, telecom operators, businesses and government agencies, exposing deep vulnerabilities in one of Asia's most digitally advanced economies. The breaches, confirmed across at least 16 financial firms and several government bodies, have compromised approximately 100,000 customer records and triggered emergency action at the highest levels of the state.
Presidential Security Leak Triggers Government Alarm
The severity of the crisis came into sharp relief when police launched a preliminary investigation into the online leak of personal information belonging to 168 individuals who travelled aboard the presidential aircraft during a trip to Europe in June. Those affected reportedly include President Lee Jae Myung, the first lady and Cabinet ministers.
In response, the foreign ministry said it is taking steps to reissue the passports of the president and first lady. The incident has raised fresh questions about how government agencies handle sensitive information and prompted broader scrutiny of state-level cybersecurity practices.
Intelligence Agency Orders Emergency Inspections Nationwide
On Tuesday, the National Intelligence Service (NIS) announced it will launch emergency security inspections at approximately 2,100 government agencies nationwide, covering central government ministries and local governments. The NIS also plans to conduct direct security checks on critical public information and communications infrastructure under its oversight, with inspections expected to be completed by mid-November.
Separately, the Ministry of Science and ICT last month raised the country's cyber crisis warning level by one notch to 'caution' — the second lowest in its four-tier system — amid global efforts to address two critical security flaws in PHP, a widely used programming language. The ministry also plans to inspect around 170 major private-sector IT infrastructure facilities to identify weaknesses before further breaches occur.
Financial Sector Hit Across Multiple Institutions
On 14 October, the Financial Services Commission (FSC) confirmed cybersecurity incidents at 16 financial firms, affecting approximately 100,000 customer records. The affected institutions included commercial banks, savings banks and credit finance companies.
The situation worsened on 28 October, when Daishin Securities, Mirae Asset Global Investments and cryptocurrency exchange Bithumb each reported separate cybersecurity incidents involving customer information. The clustering of incidents within a short window has alarmed regulators and raised concerns about systemic exposure across shared financial networks.
AI-Powered Attacks Outpace Defences
Experts say hackers are increasingly deploying artificial intelligence tools to identify security weaknesses and launch coordinated attacks on multiple targets simultaneously. This shift is particularly concerning for South Korea's highly digitised economy, where financial institutions and businesses rely heavily on shared networks and online services.
A breach at a telecom operator, for example, could expose customer data used across banking and other digital services, while an attack on a major cloud provider could cascade across multiple businesses at once. Industry experts note the risks also extend to South Korea's core manufacturing sectors — including semiconductors, automobiles and shipbuilding — which increasingly rely on connected factories and automated production systems.
Regulators Tighten Rules, But Gaps Remain
Financial regulators have announced plans to tighten identity checks and access controls, improve information sharing between institutions, and increase corporate executives' personal accountability for cybersecurity failures. Major banks, companies and government agencies have pledged to increase cybersecurity spending and strengthen security measures.
However, industry experts warn that organisations are still primarily reactive — responding after breaches rather than preventing them. The concern, according to analysts, is that AI-powered attacks could exploit vulnerabilities faster than organisations can patch them. With emergency inspections now under way and regulators tightening the framework, the weeks ahead will test whether South Korea's response can keep pace with the threat.
Point of View
But the more structurally alarming fact is that 16 financial firms were breached within weeks of each other — suggesting a systemic vulnerability in shared infrastructure, not just isolated lapses. The NIS ordering checks at 2,100 agencies is a significant escalation, but emergency inspections are reactive by nature. The harder question — whether South Korea's regulatory architecture can mandate proactive security rather than post-breach disclosure — remains unanswered. As AI tools lower the cost of launching attacks, the asymmetry between offence and defence is widening, and the country's semiconductor and shipbuilding supply chains may be the next frontier.
NationPress
3 Nov 2026
Frequently Asked Questions
What triggered South Korea's cybersecurity emergency in 2026?
A sustained wave of cyberattacks hit South Korean banks, government agencies and financial firms, compromising around 100,000 customer records across 16 institutions. The crisis escalated further when personal data of 168 people — including President Lee Jae Myung — was leaked from a presidential aircraft manifest, prompting a police investigation and NIS-led emergency inspections.
Which financial institutions were affected by the South Korea data breaches?
The Financial Services Commission confirmed breaches at 16 financial firms including commercial banks, savings banks and credit finance companies. On 28 October, Daishin Securities, Mirae Asset Global Investments and cryptocurrency exchange Bithumb each separately reported cybersecurity incidents involving customer data.
What action is the South Korean government taking in response?
The National Intelligence Service has launched emergency security inspections at approximately 2,100 government agencies, with completion expected by mid-November. The Ministry of Science and ICT raised the cyber crisis warning to 'caution' and plans to inspect 170 private-sector IT infrastructure facilities. Financial regulators are also tightening identity checks and increasing executive accountability for cybersecurity.
How does AI make these cyberattacks more dangerous?
Hackers are increasingly using artificial intelligence tools to scan for security weaknesses and launch simultaneous attacks on multiple targets, enabling them to exploit vulnerabilities faster than organisations can patch them. Experts say this shift demands a prevention-first approach rather than the reactive posture most organisations currently maintain.
Why is South Korea particularly vulnerable to large-scale cyberattacks?
South Korea's highly digitised economy means financial institutions, businesses and government agencies share interconnected networks and online services. A single breach — at a telecom operator or cloud provider — can cascade across multiple sectors. Core manufacturing industries such as semiconductors, automobiles and shipbuilding are also exposed as they rely increasingly on connected, automated systems.